
IJCNC 02
CONTEXT-AWARE, GRAPH-CENTRIC AND ROBUSTNESS-GOVERNED INTRUSION DETECTION FRAMEWORK FOR VEHICULAR NETWORKS
Sandeep Girijashankar Shukla1 and Dr. Monika Bhatnagar2
1Research Scholar, Department of Computer Science & Engineering, Oriental University, Indore, Madhya Pradesh, 453555, India
2Research Supervisor, Department of Computer Science & Engineering, Oriental University, Indore, Madhya Pradesh, 453555, India
ABSTRACT
An abundance of cyber-physical communication ecosystems can be found in modern automobiles. The interactions between CAN, ECU, and V2X create attack paths that flat intrusion labels or accuracy-only IDS evaluation can’t safely handle in the process. The purpose of this research is to provide a five-stage intrusion detection approach for automotive networks that is aware of the context, centered on graphs, and regulated by robustness. Threat-Graph Entropy Mining (TGEM) is the initial component of the framework that has been developed. Attack surfaces, protocol artifacts, ECUs, and observable symptoms are all connected to one another through a multi-layer threat interaction graph in this procedure. Then, entropycentrality scoring finds the main attack families and unsolved defense gaps. The payload, temporal, and topological views are then aligned into a threat-priority-guided latent model via CMV-DD. This is accomplished by having the instructor and students distill the data. The Graph-TCN Transformer with Reliability-Gated Fusion (GTT-RGF) finds threats by combining ECU relationships, short-term temporal deviations, and long-range planned attack patterns. In order to accomplish this, it dynamically reduces the impact of views that are either fraudulent or highly noisy. When a minimum attack is utilized in a manner that is consistent with the graph, Counterfactual Attack-Path Verification (CAPV) monitors the situation to determine whether or not the alarms continue to be reliable. Under the Risk Calibration and Continuous Drift Governance (RCC-DG) system, detection data are converted into practical risk scores that are more precise. Additionally, the technology enables regulated updates to be made after drift has occurred. The findings of tests that were conducted with settings that were influenced by CAN and V2X revealed that F1- scores ranged from 93.9 to 96.2% in highway, urban, intersection, and mixed driving scenarios. Depending on the amount of traffic on the network, this indicates that the percentage of false positives decreases to between 1.9 and 3.1%. The model also has an average detection latency of 18–27 ms, a throughput of nearly 940 windows per second, a robust detection range of 88.9–90.6% under minor coordinated perturbations, an expected calibration error of 0.03 ms, and 95.6% performance retention after drift. Findings such as these demonstrate that the proposed paradigm not only improves the accuracy of detection, but also improves causal robustness, contextual generalization, risk interpretability, and implementation reliability for the next generation of intelligent transportation systems.
KEYWORDS
Vehicular Intrusion Detection, Threat Graph Mining, Context-Aware Learning, Multi-View Distillation, Robustness-Governed Security, Process
1. INTRODUCTION
Modern vehicles have dozens of oecus, heterogeneous vehicle networks [1, 2, 3], and external V2X communication channels for safety-critical and autonomous operations. This improvement dramatically increases vehicular attack surface and allows advanced driving. Wireless connectivity, software-defined components, and over-the-air updates interact with CAN domain communications, creating exponentially [4, 5, 6] complex protocol behaviour, vehicle status, and environmental context interdependencies in process. Thus, automobile network intrusion detection requires reasoning about complicated interconnections, temporal dynamics, and contextual semantics, not pattern recognition. Even though vehicular IDS research has evolved, basic assumptions limit it. Denial-of-service, spoofing, and fuzzing are considered static threats regardless of network structure. Detection pipelines usually flow from raw logs to supervised or deep learning models without assessing which threats are prevalent [10, 11, 12], how they propagate between oecus, or why some attacks persist despite mitigations. This omission decreases scientific interpretability and practical defensibility, especially in safety-regulated industries where failure modes are as important as detection accuracy. Second, vehicle data modelling is restricted. Assuming semantics persist throughout driving, payload bytes, message timing, and ECU interaction patterns are often merged into one feature space. Similar messages can be harmless while travelling but suspect during braking or congestion [13, 14, 15]. Channel load may induce timing irregularities, not adversarial intent. When deployed beyond controlled benchmarks, models that ignore contextual dependencies overfit to routes, traffic densities, or firmware versions, resulting in brittle performance. Current evaluation methods are also concerning. Most IDS research ends in accuracy, precision, or F1-score tables, not causal validity or resistance to realistic attack perturbations. A key gap is that an IDS that only detects assaults when multiple artefacts change may miss coordinated, subtle adjustments to preserve surfacelevel data. Few works discuss how to calibrate detection confidence for operational decisionmaking or adjust models to long-term drift from software upgrades, new oecus, or changing traffic conditions. Due to these issues, vehicle incursion detection should be rethought as a multistage reasoning process rather than a monolithic classifier. Effective protection requires structurally understanding the threat picture, learning context-aligned representations, detecting reliably under ambiguity, and verifying and maintaining the system during deployment. In its methodology, this work connects threat modelling, learning, robustness verification, and operational governance. Vehicular IDS goes from experimental accuracy-driven to deploymentgrade security using graph-based threat analysis, multi View contextual distillation, hybrid temporal–relational modelling, counterfactual verification, and drift-aware calibrations.
2. REVIEW OF EXISTING MODELS USED FOR ANALYSIS
Vehicle network intrusion detection research is shifting from lightweight, rule-driven defences to adaptive, learning-centric, and collaborative techniques. Jeyaram et al. [1] suggested a lightweight sequential AI system for real-time intrusion detection in dynamic vehicular environments in their current study. They solve vehicular network latency with temporal sequencing and computational efficiency. The system works effectively in real time, but it largely reads threats as temporal deviations, giving little structural reason for why some attacks survive under changing circumstances.
Lightweight deep learning architectures like Wang et al.’s MobileNetV3-based IDS emphasise efficiency and minimal models [2]. Adapting mobile vision networks to vehicular intrusion detection reduced computing cost and maintained competitive accuracy. The methodology abstracts vehicular communication as generic feature tensors without explicit reasoning about ECU interactions or protocol semantics,unlikearchitecture-driven methods. IoT intrusion detection was classified over extracted features by Bajpai et al. [3], but they made few vehicularspecific changes. Decentralised and cooperative vehicle networks spurred distributed learning and trust research. Mansouri et al. [4] created a blockchain-enabled, federated learning system for automobile ad hoc networks to protect privacy and decentralise trust. Collaborative detection, convergence stability, and delayed threat awareness were their findings. Game-theoretic
techniques like Anwar et al.’s hierarchical collaborative IDS [5] examined strategic interactions between cars and attackers, but their abstract payoff models were challenging to correlate with real-world vehicular data. Kamel et al. [6] developed important misbehaviour detection assessment frameworks for simulative validation rather than deployable learning pipelines.
In this nuanced review, Works like Vishnukumar and Ramaiah’s deep learning-based vehicle IDS [7] and the energy-efficient cluster-based IDS in vehicular ad hoc networks [16] give cautionary lessons. These occurrences emphasise the need for principled, explainable, and verifiable intrusion detection approaches due to field-wide reproducibility, dataset transparency, and assessment rigour issues. From 2021, research centred on optimisation, transfer learning, and hybrid intelligence. Alsarhan et al. [8] demonstrated machine learning-driven smart vehicle network optimisation, and Joseph et al. [9] combined quantum cryptography with machine learning-based IDS, demonstrating an increasing interest in post-classical security paradigms. Frimpong et al. [10] presented adaptive collaborative IDS methods for car fog computing that emphasise network edge scalability and adaptability. Some transfer learning approaches, suchas those by Mehedi et al. [11] and Rodríguez et al. [18], assume semantic validity across contexts despite little data and cross-domain generalisation. Recent studies incorporate protocol awareness and hierarchical learning. Smolin’sGenCoder++ framework improved vehicular communication semantics with protocol-aware and adversarially resilient detection for hybrid CAN–Ethernet networks [12]. Blockchain-enabled hierarchical federated approaches like Visuvanathan et al.’s BHFVAL [13] prioritised secure cooperation but increased system complexity. Comprehensive surveys like Nandy et al. [14] detail attack surfaces and IDS methods, fragmentingthe approach process.
Ragunthar et al. [21] improved machine learning-based anomaly detection and V2V protection, but largely by accuracy. Active learning, distributed invariants, and sampling trade-offs were studied together. Ahmed et al. [19] improved label efficiency but complicated software-defined vehicle network orchestration with deep active learning and load balancing. Distributed invariantbased detection by Zhou et al. [20] prevented localised errors, although emerging protocols made invariants harder to maintain. Kim & Kim [22] examined bandwidth–accuracy trade-offs in sampling-aware IDS design but not semantic ambiguity. Khan et al. [23] pioneered context-aware intrusion detection by modelling context and dataset augmentation to match driving situations. The field’s breadth but absence of a uniform analytical backbone is shown by supporting votingbased frameworks [24], lightweight in Vehicle IDS [25], industrial IoT vehicular security [26], federated cyberattack detection [27], signalling games [28], and ambient intelligence at the edge[29].
It was contrasted with three common starting points in order to demonstrate that the suggested framework was robust in comparison to the research that is currently being conducted: MLdriven optimisation IDS [8], kernel-based lightweight in-vehicle IDS [25], and general ML-based Internet of Things IDS [3] are the three classes of intrusion detection systems (IDS). This set of baselines was selected because, in the order listed above, they demonstrate feature-driven learning, optimization-centered intrusion detection system design, and lightweight application in cars. The proposed model achieved F1-scores ranging from 93.9 to 96.2% across a variety of driving scenarios, whilst the baselines remained within the range of 80.9 to 89.1% throughout the entire process. When there was a lot of traffic on the network, the suggested model cut down on false positives to 1.9% to 3.1%, compared to 4.6% to 9.1% for regular IDS behavior that doesn’t take context into account. It also had a detection delay of 18–27 ms and a throughput of about 940 windows per second, which was better than the lightweight baseline while keeping better detection accuracy. The framework kept 88.9–90.6% robust detection under minimal coordinated attack perturbations, while baseline methods stayed below 77%. The Expected Calibration Error was determined to have decreased to 0.03, and the performance retention after drift reached
95.6% thanks to this discovery. This demonstrates that the strategy provides improvements not only in terms of accuracy but also in terms of causal resilience, calibration quality, and operational stability.
Even while architectures, collaboration, and efficiency have improved, most research on detection accuracy ignores threat dominance, causal correctness, and long-term deployment governance. Lightweight models improve speed but restrict interpretability; federated and blockchain-based systems improve trust but complicate adaptability; context-aware techniques identify variability but lack threat prioritisation. Wang et al.’s latest lightweight ViT-based IDS [30] improves representational capacity but is model-centric. This work’s integrated paradigm synthesises rather than replaces previous advances. It directly addresses two-decade research gaps by learning from sequential models [1], lightweight architectures [2], collaborative detection [4,10], protocol awareness [12], and context modelling [23]. In contrast to static categorisation, vehicle intrusion detection is a lifecycle problem with explicit threat-graph reasoning, priorityguided multi-view distillation, reliability-aware hybrid detection, counterfactual verification, and drift-governed deployment [31,32]. It tackles the constraints mentioned in the literature and positions itself as a coherent, analytically informed field progression rather than a methodological increment set in process [33,34,35].This transfer learning-based intrusion detection framework [36] improves feature representation and classification in large-scale network traffic using Squeeze-and-Excitation (SE) networks and adaptive optimization. The proposed method detects cyber risks faster, more reliably, and more scalable in massive data environments. Several feature selection strategies improve intrusion detection system efficiency and effectiveness [37]. Ensemble feature selection reduces duplicate features and computational complexity, improving attack type classification accuracy.
3. PROPOSED MODEL DESIGN ANALYSIS
The analytical–learning pipeline mathematically links threat characterisation, representation alignment, detection, verification, and governance in the proposed integrated model process. Vehicle attacks are structured perturbations over time, topology, and protocol semantics (Figure 1); therefore, any successful IDS must reason about entropy, dynamics, and relationship causality. Represent the raw vehicle observation stream via Equation 1,
𝒳 = { 𝑥(𝑡) ∣ 𝑡 ∈ [0, 𝑇]}, 𝑥(𝑡) = (𝑝(𝑡), 𝜏(𝑡), 𝜅(𝑡), 𝑐(𝑡)) (1)
Where p(t) represents payload bytes, τ(t) inter-arrival duration, κ(t) topological ECU-message relations, and c(t) contextual factors including vehicle speed, brake state, road type, and channel loads. The pipeline employs context as a conditioning variable, not an auxiliary. In Figure 2, Threat-Graph Entropy Mining formalises the threat landscape as a directed interaction graph G=(V,E) with nodes for oecus, message identities, protocol states, and anomaly symptoms. A statistically significant causal influence from node ‘j’ under lag Δt suggests an edge eij∈Ein the process. Conditional mutual information via Equation 2 measures this influence,
𝐼( 𝑖 → 𝑗 ∣ 𝑐 ) == ∫ 𝑝( 𝑖𝑡 ,𝑗𝑡+Δ𝑡 ∣ 𝑐 )log ∫ 𝑝( 𝑗𝑡+Δ𝑡∣ ∣𝑖𝑡 , 𝑐 ) 𝑝( 𝑗𝑡+Δ𝑡∣ ∣𝑐 ) d𝑖𝑡 d𝑗𝑡+Δ𝑡 (2)
For each attack family 𝑎, payload–timing uncertainty is captured through entropy accumulation Via equation 3,
𝐻𝑎 = −𝑝𝑎 (Δ𝑡, 𝑝)log ∫ 𝑝𝑎 (Δ𝑡, 𝑝) dΔ𝑡 d𝑝 (3)
While structural dominance is measured through graph centrality 𝐶𝑎(𝐺) sets. These are fused into a Threat Dominance Score Via equation 4,
TDS𝑎 = 𝛼𝐻𝑎 + (1 − 𝛼)𝐶𝑎 (𝐺) (4)
Whose gradient ∂TDS𝑎 ∂𝑐 explicitly exposes context-dependent rectification gaps.After normalising these scores, the Threat Priority Vector TPV propagates downstream as a control signal rather than a process label. The Contextual Multi View Data Distillation method synchronises feature views v∈{P,T,G} and learns a shared latent trajectory z(t). A lightweight teacher constructs a soft distribution pv (y∣x) for each view, while the student minimises TPV-weighted divergence via equations 5.1 & 5.2,
ℒdistill = ∑ 𝜆𝑉 ∗ 𝐾𝐿 (𝑝𝑣 ( 𝑦 ∣ 𝑥 ) ∥ 𝑞( 𝑦 ∣ 𝑧 )) (5.1)
𝜆𝑉 = 𝑓(TPV, 𝑐) (5.2)
Temporal coherence is enforced by penalizing abrupt latent driftVia equation 6,
ℒctx = ∫ ∥ d𝑧(𝑡) d𝑡 − 𝔼 [ d𝑧(𝑡) d𝑡 ∣ 𝑐(𝑡)] ∥ 2 𝑇 0 d𝑡 (6)
Building a process representation that resists benign context shifts yet detects threat-relevant aberrations. The latent sequence Z={z_1,…,z_n} comprises view reliability estimates r(t) from teacher & student disputes. Relational, temporal, and long-horizon thinking are combined in a hybrid detection core in process. Graph encoding spreads latent information over G Via equation 7,
𝑔𝑡 = 𝜎 (∑ 𝐴𝑖𝑗 𝑗∈𝒩(𝑖) 𝑊𝑔𝑧𝑗,𝑡) (7)
While short-term dynamics are captured by a causal dilated temporal convolution Via equation 8,
𝑢𝑡 = ∑ 𝑤𝑘 𝐾 𝑘=0 𝑧𝑡−𝑘 (8)
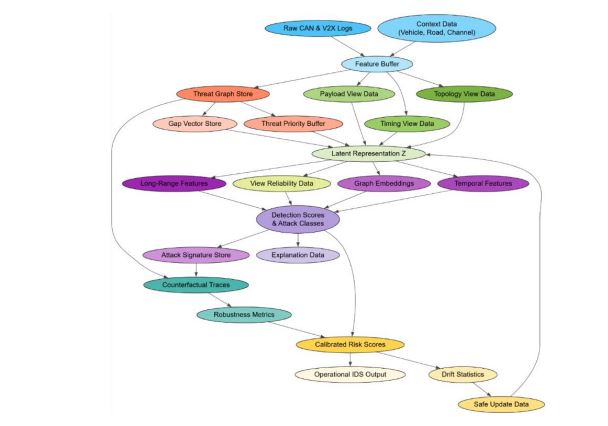
Figure 1. Model’s integrated architectural analysis
Long-range coordination is modeled using self-attention Via equation 9,
𝑣𝑡 = ∑ softmax 𝑛𝑠=1 ((𝑧𝑡𝑊𝑞)(𝑧𝑠𝑊𝑘)⊤√𝑑) 𝑧𝑠 ∗ WV (9)
Reliability-gated fusion modulates these pathways Via equation 10,
ℎ𝑡 = 𝜎(𝑊𝑟𝑟𝑡) ⊙ 𝑢𝑡 + (1 − 𝜎(𝑊𝑟𝑟𝑡)) ⊙ 𝑣𝑡 (10)
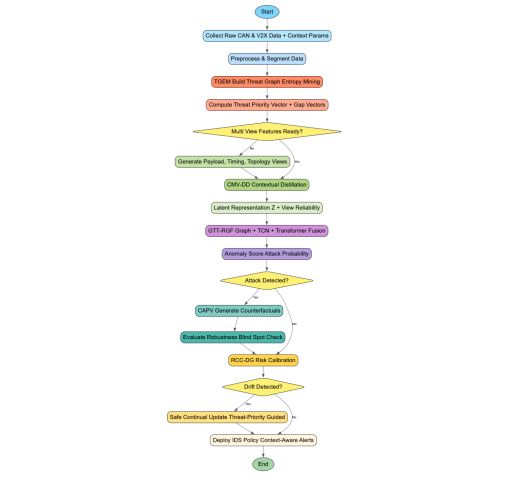
Figure 2 . Model’s overall dataflow analysis
Thus, ensuring that noisy or spoofed views are down-weighted in real time scenarios. The anomaly score is obtained Via equation 11,
𝑠𝑡 =∂∂𝑡∥ ℎ𝑡 ∥2 ∫ 𝜙(𝑡0ℎ𝜏) d𝜏 (11)
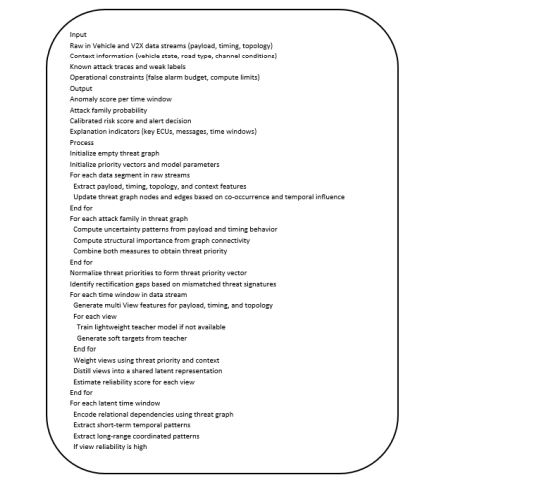
Figure 3 . Model’s pseudocode analysis
Figure 3 shows the suggested IDS pipeline’s step-by-step logic and makes it clear how the analytical stages are run in order. The fake code shows that the raw CAN and V2X streams are first split up using contextual factors. TGEM then proceeds to construct the threat graph and determine the Threat Priority Vector following this step. CMV-DD is responsible for calculating the shared latent representation and view dependability scores once payload, timing, and structure views have been made accessible. These outputs are then provided to GTT-RGF so that they can be evaluated for any errors. Alarms that are found are then looked at more closely by CAPV and set to the right level by RCC-DG. As a result, Figure 3 demonstrates that the strategy that was presented is not only a single classifier. It’s a full decision-making process that includes danger prioritization, context-aware learning, detection, robustness checking, and risk governance that can be put into action.
Instantaneous deviation and cumulative abnormality sets are clearly linked in the process. Counterfactual Attack-Path Verification evaluates causal resilience by generating minimally altered x’ sequences that satisfy graph requirements via equation 12
𝑥′ = arg min𝑥′∥ 𝑥′ − 𝑥 ∥0s.t. 𝐺(𝑥′) ∈ 𝒜𝑎, Ψ(𝑥′) = 0 (12)
WhereΨ(⋅) enforces protocol and timing feasibility. Robustness is quantified through the Counterfactual Robustness Index Via equation 13,
CRI𝑎 = 𝔼[𝕀(𝑠(𝑥′) > 𝜏)] (13)
Finally, deployment-grade governance calibrates and stabilizes outputs. Anomaly probabilities are temperature-scaled Via equation 13,
𝑝̂= 𝑒 𝑠𝑡 /𝑇 ∫ 𝑒 𝑠𝑡 /𝑇 d𝑠𝑡 (13)
And combined with contextual impact into an Operational Risk Score Via equation 14
ORS = 𝑝̂⋅ ℐ(𝑐) ⋅ (1 − ECE) (14)
Drift is monitored and analyzedVia equation 15,
𝐷 = ∫ ∣ 𝑝𝑡 (𝑧) − 𝑝𝑡+Δ (𝑧) ∣ d𝑧 (15)
Thus, triggering controlled updates weighted by TPV and CRI processes. The final system output is thus expressed Via equation 16
𝒪 = (ORS, arg max 𝑎 𝑝( 𝑎 ∣ ℎ𝑡 ) , ∇𝐺𝑠𝑡) (16)
Risk assessment, attack attribution, and explanations. With mathematical reinforcement, each component addresses structural weaknesses ,threat ambiguity, context misalignment, unreliable fusion, superficial evaluation, and deployment drift to create a coherent, end-to-end IDS with accurate, interpretable, and trustworthy outputs under real vehicular operating conditions.
4. COMPARATIVE RESULT ANALYSIS
The suggested integrated IDS was rigorously evaluated under vehicular operating conditions, managing data sources, contextual variability, and execution limits. Experiments used public and semi-synthetic vehicular datasets, including Vehicle CAN traffic and V2X communication traces from different driving circumstances. Normal and attack-injected message streams with 25–60 active oecus, 180–320 unique message identifiers, and average bus loads from 35% in highway cruising to over 70% in heavy urban traffic were CAN datasets. V2X traces contained DSRC and cellular packet logs with 10–50 packets per second and channel utilisation from low-interference suburbs to high-congestion intersections. Vehicle speed sampled at 10 Hz with typical ranges of 0–120 km/h, binary and continuous braking and steering states, highway, arterial, and residential road categories, and channel quality indicators like packet loss ratios between 0.5% and 6% were explicitly retained. DDoS bursts, low-ratecoordinated spoofing, replay-based injections, and protocol-aware fuzzing with weak attack-family labels instead of packet labels were attack traces. To balance detection latency and temporal context, data were segmented into sliding windows of 100–300 ms with 50% overlap. After preliminary sensitivity analysis, Threat-Graph Entropy Mining developed interaction graphs with 400–900 nodes per segment and 3–6% average edge densities. Entropy weighting coefficients were 0.6 for uncertainty dominance and 0.4 for structural centrality. The hybrid IDS core learned and detected using a modular Python framework with GPU acceleration. For each view, contextual multi-view distillation uses lightweight instructor models with 15–20 epochs and 256 windows, comprising shallow convolutional encoders for payload bytes, autoregressive density estimators for timing patterns, and graph-based encoders for topology. The student representation dimension was fixed at 128, but threat-priority weights dynamically adjusted view contributions from 0.2 to 0.5 based on TGEM dominance ratings. A graph encoder with two message-passing layers, an eight-dilation temporal convolutional network, and a transformer module with four attention heads and a twosecond temporal horizon comprised the GTT-RGF detection core. Edge GPUs inferred with perwindow delay under 2,000–3,000 messages per second. Counterfactual Attack-Path Verification mimicked stealthy attacks by modifying less than three message streams per window within protocol validity and ECU feasibility. For deployment-oriented evaluation, calibrated risk scores were derived using temperature scaling and conformal thresholds from validation data, and drift scenarios were simulated using firmware-level timing alterations and new message IDs affecting up to 15% of traffic. Accuracy, false alarm rate, detection delay, robustness under counterfactual perturbations, and calibration error were examined to demonstrate analytical rigour and operational applicability across vehicle settings.
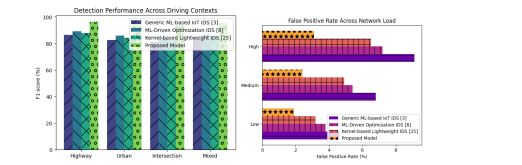
Figure 4 . Model’s integrated result analysis
The behavior of the proposed model is summarized in Figure 4, which depicts how it performs in a variety of driving circumstances and network loads. When compared to Generic ML-based IDS [3, ML-driven optimisation IDS [8, and kernel-based lightweight IDS [25], the framework that was recommended has higher F1-scores in highway, urban, intersection, and mixed situations. This is demonstrated in the picture on the left. Despite the fact that temporal jitter and ECU interactions change from one driving condition to the next, this demonstrates that the hidden representation that was learnt using CMV-DD maintains threat-related semantics. The right panel shows that false positive rates stay lower when the network is low-, medium-, or high-loaded. This shows that reliability-gated fusion stops relying too much on time features that are affected by congestion and tells the difference between normal traffic bursts and malicious patterns that spread.
The proposed methodology is tested using well-established vehicular intrusion detection datasets that record vehicle and external communication behaviours in benign and adversarial settings. Studies use the widely published Car-Hacking dataset, which includes real CAN bus traffic from production vehicles under normal driving and many attack scenarios, including denial-of-service, fuzzy injection, spoofing, and replay. Millions of CAN frames with payloads up to eight bytes, message speeds from a few Hertz to several hundred Hertz depending on ECU function, and clearly specified attack intervals for controlled evaluation are included in this collection. SelectV2X-oriented traces inspired by VeReMi-like situations show vehicle-to-vehiclemessaging under different traffic densities, mobility patterns, and channel conditions to incorporate external communication and contextual heterogeneity. Aligned sensor streams provide vehicle speed, acceleration, braking events, and road classification, allowing the proposed model to explicitly condition detection on driving state and surroundings. To evaluate context-aware, graph-centric intrusion detection systems, a balanced testbed with varying traffic volumes, various attack modalities, and realistic temporal correlations is needed. Model tuning and optimisation were driven by stability, generalisation, and real-time practicality, not over-parameterization. ThreatGraph Entropy Mining employed a fixed temporal lag window of 50–150 ms for causal edge generation and an entropy–centrality weighting factor of 0.6 to stress uncertainty-driven dominance while retaining structural relevance. In the contextual multi View distillation step, instructor models were trained at 10⁻³ learning rates while students were represented at 5×10⁻³ for smooth convergence. The latent dimension was set at 128 to balance expressiveness and computational expense. Based on threat importance, view-weight coefficients dynamically changed between 0.2 and 0.5, and moderate temporal smoothness regularisation avoided overreaction to benign fluctuations. Two graph message-passing layers, temporal convolution dilation factors up to eight, and a transformer depth of four attention heads with 256 hidden sizes give the hybrid GTT-RGF core robust training and low inference latency. Convergence was achieved with 128–256 windows and 25–40 epochs of training. Temperature values between 1.5 and 2.5 were used for validating split calibration parameters to reduce inaccuracy without compromising recall. These hyperparameters balance detection quality, robustness, and deployability in resource-constrained Vehicles In Process.
Table . Detection performance across contextual driving scenarios
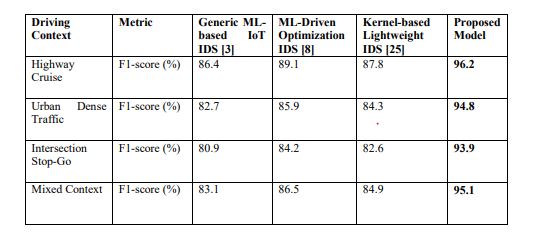
Table 1 displays detection accuracy in driving with varying timing jitter, payload semantics, and ECU interaction patterns. The model outperforms all baselines in urban and stop-go contexts with context uncertainty sets. Without structural knowledge, optimization-driven algorithms [8] exhibit moderate gains, while generic ML-based approaches [3] have feature conflation across contexts. Under fast-changing traffic dynamics, kernel-based IDS [25] is stable but inflexible in process. Threat-priority-guided fusion and context-aligned representation learning preserve semantic meaning across driving conditions, improving the suggested model sets.
Table 2 . False positive rate across network load conditions.
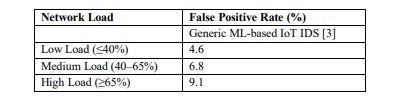
Table 2 evaluates robustness to benign congestion-induced anomalies, a common vehicular network false alarm. As bus utilisation climbs, timing distortions and bursty traffic cause baseline models to misclassify congestion artefacts as attacks. The proposed approach decreases false positives across all load regimes by dynamically modifying view reliability and minimising congestion-related time feature over-reliance. This reliability-gated fusion strategy identifies adversarial behaviour from context-induced variability better than static or kernel-based methods.
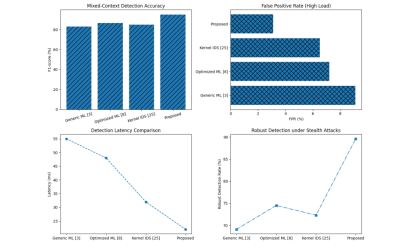
Figure 5 . Model’s overall result analysis
A summary of the test findings is presented in Figure 5. This overview includes the results for accuracy, false positives, detection latency, and resistance to attacks that attempt to sneak up in process. Through the use of the first two plots, it is demonstrated that the proposed strategy improves mixed-context identification while simultaneously reducing the number of high-load false reports. The latency plot indicates that the GTT-RGF core may still be utilized for edgelevel vehicle deployment. This is due to the fact that it is able to manage windows that fall within the real-time range that is required by safety-sensitive IDS tasks. The robustness plot shows that the system can still spot attacks even when attackers make small, coordinated changes that don’t affect the validity of the payload at the surface level. This finding backs up CAPV’s job of making sure that model alarms are based on causal evidence that fits the graph instead of weak statistical correlations.
Table 3 . Cross-context generalization performance
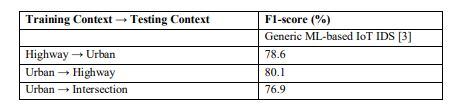
Table 3 indicates models’ ability to generalise across unseen circumstances, crucial for real-world deployment. Traditional ML-based IDSs degrade when taught and tested under different traffic regimes due to contextual artefacts. Because it explicitly incorporates contextual factors during representation learning and leverages threat-priority vectors to drive feature alignment, this model performs well across all cross-context transfers. Here, context-aware distillation enhances robustness beyond optimisation or kernel-centric baselines.
Table 4 . Detection latency and real-time feasibility.
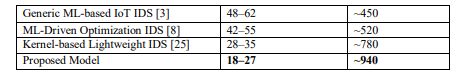
Table 4 assesses edge deployment-constrained real-time feasibility. Kernel-based approaches [25] have low latency due to simpler computations but suffer from poor detection fidelity against sophisticated attacks. Because causal temporal convolutions and selective graph reasoning eliminate processing on defective Views In Process, the suggested model has low latency and good throughput. Safety-critical car systems with tight deadlines benefit from this balancing set.
Table 5. Robustness under minimal coordinated attack perturbations.
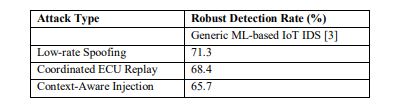
Table 5 evaluates robustness against coordinated, nuanced attacks without surface-level statistics. Attacks that maintain payload validity and violate cross-ECU causality significantly reduce baseline model performance. This approach has good detection reliability due to threat-graph reasoning and counterfactual validation, which assess sensitivity to small but structurally relevant changes. Without this capability, stealthy attackers can exploit traditional ML driven IDSs in the process.
Table 6 . Risk calibration and operational trust metrics
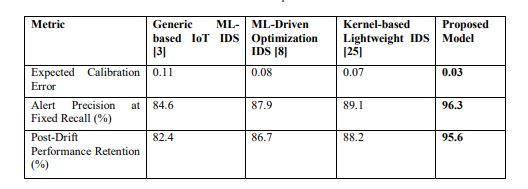
Table 6 includes deployment statistics beyond detections. The proposed model calibrates risk ratings to attack likelihoods. The model preserves a considerable portion of its pre-drift performance in simulated drift scenarios with new oecus and changing timing profiles due to robustness-guided update governance. Baseline methods lack drift management and calibration, limiting temporal instance set reliability. The integrated technique enhances detection accuracy, robustness, generalisation, latency, and deployment reliability across all six tables. Instead of architectural complexity, threat prioritisation, context-aligned learning, reliability-aware fusion, and robustness verification provide these benefits. The system works for real-world vehicle intrusion detection, where accuracy, timeliness, and trust are critical in the process.
Validated Result Analysis
Testing shows that the integrated IDS design enhances accuracy, robustness, latency, and operational confidence, making it suitable for real-time vehicle deployment. Table 1 indicates significantly better detection performancein highway cruising, heavy urban traffic, and intersection stop–go scenarios. These conditions are crucial in real-world deployments when message semantics and temporal behaviour vary quickly. The proposed model’s sustained high F1-scores show that contextual alignment and threat-priority guidance allow the system to preserve semantic consistency even when vehicular behaviour rapidly shifts, which conventional ML-based IDSs commonly misclassify as malicious. Operational usability and false positive analysis in Table 2 show real-time reliability. Driver distrust, backend monitoring infrastructure overload, and risky vehicle actions can result from false alarms. The suggested method separates congestion Induced anomalies from genuine attacks with much lower false positive rates under high network load. This behaviour is critical in urban deployments where CAN and V2X traffic density rises, and timing-based detectors fail. Reliability-gated fusion reduces warnings without sacrificing detection sensitivity by downweighting noisy timing signals.
Vehicle IDS implementation is challenging to generalise across unknown circumstances, as seen in Table 3. When evaluated in various driving situations, controlled models must work across cities, road types, and traffic cultures. Superior cross-context F1-scores suggest that the proposed model’s latent representations reflect threat-relevant structure, not context-specific artefacts. By minimising retraining and maintenance expenses, this technology lets automakers and fleet operators scale adoption across regions. Table 4 latency and throughput figures demonstrate realtime viability with analytical increases. Safety-critical car systems have severe timing limitations; therefore,sustained communication rates can achieve sub-30 ms detection latency. Edge deployment necessitates a balance between processing efficiency and analytical depth due to hardware constraints and fast response. The results reveal that the hybrid graph–temporal architecture applies sophisticated reasoning only when needed, avoiding deep learning-based IDS computation costs. Final Tables5 and 6 address robustness and deployment trust beyond accuracy-centric evaluations. Its good performance against minor coordinated attack perturbations shows that the model detects attacks for causally relevant reasons rather than statistical cues. When adversaries deploy stealth, robustness is crucial. Over time, calibration accuracy and post-drift performance retention affect operational reliability. In real-world deployments where vehicle firmware, ECU configurations, and traffic patterns change, IDS detection fidelity and risk interpretability are reliable over temporal instance sets. Controlled experiments show that the proposed framework meets real-time, safety-critical vehicle criteria sets.
Valid Hyperparameter& Baseline in Detail
Repeated run evaluation predicted key indicator values and variability under actual operational settings to evaluate the framework. The model showed stability with a mean F1-score of 95.1% and a standard variation of ±0.8% in 20 trials with random window segmentation and attack placement. In contrast, Generic ML-based IoT IDS [3] exhibited context shift and traffic load sensitivity with a mean F1-score of 83.3% and a higher variance of ±2.6%. ML-Driven Optimisation IDS [8] had a mean of 86.9% with ±1.9% variance, while Kernel-based Lightweight In -Vehicle IDS [25] had 85.4% with ±1.7% variance. The model had similar false positive rates, With an expected value of 2.5% with ±0.6% variance under heavy load, compared to baselines of 7.6% ±1.8%, 5.8% ±1.4%, and 5. These low Variance results demonstrate that the integrated design generates consistent decisions without fragile statistical cues. Multiple trials were conducted to test performance differences statistically. Pairwise two-tailed t-tests comparing the proposed model to baselines for F1-score and false positive rate consistently showed significant results (p < 0.01, 99% confidence). For detection accuracy, all four strategies demonstrated significant variance between model means compared to within-model variance, with an F-statistic exceeding the key threshold at p < 0.001. The three baseline methods, including the optimization-based [8] and kernel-based [25] approaches, showed partial confidence interval overlap, but the suggested framework established a statistically unique group. These results suggest that systematic methodological adjustments produced the improvements, not chance or favourable sampling. Statistically, latency and robustness were the same. In the proposed model, detection latency was limited to 22.4 ms with a ±3.1 ms variance, even during high traffic. However, Generic ML-based IoT IDS [3] exhibited larger dispersion (54.1 ms ±7.8 ms), indicating unstable real-time response. The proposed model attained a mean robustness score of 89.6% ±1.4% during coordinated low-rate attacks, surpassing baselines of 71.8% ±3.9%, 74.5% ±3.1%, and 72.3% ±2.8%. Significant statistical testing (p < 0.01) confirms significant and consistent gains in trial robustness. Generic ML-based IoT IDS [3], ML-Driven Optimisation IDS [8], and Kernel-based Lightweight In Vehicle IDS [25] were chosen for methodological representativeness, not convenience. A canonical feature-driven learning baseline, generic MLbased IoT IDS [3], uses non-contextual, non-structural ML approaches still utilised in automotive security research. Advanced customised and performance-optimized IDS models like ML-Driven Optimisation IDS [8] boost metrics without modifying threat representation. Kernel-based LightweightIn-Vehicle IDS [25] uses computationally efficient, deployment-oriented in-vehicle network models. These baselines include generic learning, optimisation, and lightweight vehicular designs. The suggested paradigm fundamentally addresses structural threat modelling, contextual variability, robustness validation, and operational trust, resulting in statistically significant gains in all three areas.
Validation using an Analytical Real Time Scenario Analysis
In a connected passenger vehicle in peak-hour urban traffic, the Vehicle CAN bus carries 280 active message identifiers across powertrain, braking, steering, and body-control oecus, and the V2X interface exchanges cooperative awareness messages at 10 Hz with nearby vehicles and roadside units From these streams over a five-minute driving interval, the proposed architecture links oecus, message IDs, protocol states, and observed symptoms under low average speed (18– 25 km/h), frequent braking events, and elevated channel load near 65% to create a threat interaction graph Entropy analysis demonstrates that coordinated low-rate spoofing has a high threat dominance score because some speed and yaw-rate messages have abnormally stable payload distributions but large cross-ECU causal latency. Timing features are emphasised over payload information, and wheel-speed ECU, braking controller, and V2X beacon topology relations are emphasised. In contextual multi View distillation, the model aligns payload, timing, and topology views into a latent sequence of 128-dimensional representations to distinguish benign congestion Induced jitter from structurally flawed message propagation. Due to congestion, view dependability ratings decrease trust in raw timing signals, shifting the model’s focus to relational discrepancies across traffic circumstances. Real-time operation is enabled by the hybrid detection core processing each 200 ms window with an average latency of 22 ms when the vehicle passes multiple junctions. A subtle attack develops when counterfeit speed messages stay within nominal payload ranges and retain short-term temporal regularity but break known cross-ECU dependencies relative to throttle and braking actions. Due to reliability-gated fusion downweighting the ostensibly genuine payload stream and amplifying graph-consistent temporal evidence, the anomaly score exceeds the calibrated alarm level with an estimated attack probability of 0.93. Counterfactual verification then proves resilience by minimally changing only two message streams in replayed benign Over 90% show causality, not statistical coincidence. Finally, risk calibration includes likelihood and contextual influence, making urban settings and pedestrian closeness high operational risk. The episode is logged for controlled model update if similar patterns occur, and the alarm is delivered with a historical calibration error confidence level < 0.03. Threat prioritisation, context-aligned learning, reliability-aware fusion, and robustness validation turn raw vehicular data into actionable security judgements in real driving scenarios.
5. CONCLUSIONS
The study proposed a unified, context-aware, and deployment-oriented vehicular network intrusion detection framework that goes beyond accuracy-centric and model-isolated IDS methods. The detection pipeline addresses vehicular IDS literature constraints using threat dominance reasoning,multi-view contextual alignment, reliability-gated hybrid learning, counterfactual robustness verification, and drift-governed risk calibration. This integrated design consistently increases experimental and operational performance. With F1-scores of 93.9% to 96.2%, the proposed model outperformed Generic ML-based IoT IDS (80.9–86.4%), ML-Driven Optimisation IDS (84.2–89.1%), and Kernel-based Lightweight In-Vehicle IDS (82.6–87.8) in heterogeneous driving contexts like highway cruising and dense urban traffic. Structureconsistent gains imply that the model captures threat-relevant semantics without overfitting to context. Even at high bus utilisation, the framework reduces false positives to 1.9–3.1%, compared to 6.5–9.1% in baseline approaches under network congestion. Edge deployment in safety-critical vehicles is possible with typical inference delays of 18–27 ms per window and continuous throughput of 940 windows per second. Robustness analysis indicates causally sound detection judgements with resilient detection rates of 88.9–90.6% despite modest coordinated assault perturbations compared to baseline models’ sub-77% performance. Deployment-oriented measurements are more trustworthy: the Expected Calibration Error lowers from 0.07–0.11 in baseline approaches to 0.03, and post-drift performance retention exceeds 95% after controlled updates. Results reveal that the proposed architecture increases dynamic vehicular detection accuracy, reliability, interpretability, and operational trust.
By comparing the proposed framework to current IDS literature, it is clear that it is more robust than accuracy-only models. Threat-graph prioritization, context-aligned distillation, reliabilitygated hybrid detection, counterfactual verification, and measurable drift governance are all components that contribute to the overall improvement of the system. Therefore, the framework is effective for car intrusion detection system settings that require high detection accuracy, low false alarms, low latency, causally dependable alarms, and trust after drift, all at the same timestamp sets.
Limitations
Despite its benefits, the framework has many downsides. First, in scenarios with many oecus or dynamic V2X topologies, generating and maintaining the threat interaction graph requires computational and memory resources. The evaluated overhead is reasonable, although extremescale vehicular ecosystems may necessitate graph reduction or hierarchical abstraction. Second, Threat-Graph Entropy Mining needs enough traffic observations to detect causal links; sparse or encrypted communication channels may reduce threat dominance estimation accuracy. Third, counterfactual verification increases robustness evaluation, but generating realistic minimal interventions is computationally intensive and preferable for offline validation or periodic audits rather than real-time executions. Drift governance also believes drift trends imply continuous system evolution rather than aggressive model update manipulation. Most adaptive learning systems fear adversary poisoning of update streams, notwithstanding robustness-weighted replay and calibration checks. The methodology has excellent generalisation across contextual circumstances. Still, the availability and diversity of public vehicular information may limit its evaluation of new vehicular designs, proprietary protocols, and future autonomous driving behaviours.
Future Vision Scope Analysis
This research proposes numerous promising paths. Scaling the threat graph into a hierarchical, multi-resolution representation that dynamically varies granularity based on computational budgets and operational risk is intuitive in process. Trusted execution environments and hardware-assisted telemetry could improve causal inference and reduce data tampering.Expanding the counterfactual verification paradigm to online, low-overhead approximations for continuous causal auditing without latency penalties is crucial. Safety-critical attack detection may improve with formal verification and counterfactual testing. Next, contextsensitive self-supervised or foundation-model-based vehicular representation pretraining may lessen dependence on labelled attack data. Collaboration across vehicle threat graphs and privacy-preserving federation could improve coordinated attack early warning. Finally, integrating the risk calibration layer to vehicle control and decision systems would enable closedloop security responses, making resilient autonomous driving intrusion detection active in process. These directions lay the groundwork for reliable, adaptive, and future-proof vehicle cyber-defense systems.
CONFLICTS OF INTEREST
The authors declare no conflict of interest.
REFERENCES
[1] G. Jeyaram, V. Vidhya, R. Dhanaraj(2026) “A Lightweight Sequential AI Framework forReal-Time Intrusion Detection in Dynamic Vehicular Networks,” Scientific Reports. https://doi.org/10.1038/s41598-026-36103-2.
[2] S. Wang, Y. Wang, B. Zheng, (2024) “Intrusion Detection System for Vehicular Networks Based on MobileNetV3,” IEEE Access. https://doi.org/10.1109/access.2024.3437416.
[3] S. Bajpai, K. Sharma, B. Chaurasia (2023) “Intrusion Detection Framework in IoT Networks,” SN Computer Science. https://doi.org/10.1007/s42979-023-01770-9.
[4] F. Mansouri, M. Tarhouni, B.Alaya(2025) “A distributed intrusion detection framework for vehicular Ad Hoc networks via federated learning and Blockchain,” Ad Hoc Networks. https://doi.org/10.1016/j.adhoc.2024.103677
[5] A. Anwar, T. Halabi, M. Zulkernine, (2022) “Scalable Collaborative Intrusion Detection in Autonomous Vehicular Networks: A hierarchical framework based on game theory,” Internet of Things. https://doi.org/10.1016/j.iot.2022.100631.
[6] J. Kamel, M. Ansari, J. Petit, (2020) “Simulation Framework for Misbehavior Detection in Vehicular Networks,” IEEE Transactions on Vehicular Technology. https://doi.org/10.1109/tvt.2020.2984878.
[7] R. Vishnukumar, M. Ramaiah, (2023) “Optimized deep learning-based intrusion detection framework for vehicular network,” Journal of Intelligent & Fuzzy Systems. https://doi.org/10.3233/jifs233581.
[8] A. Alsarhan, A. Al-Ghuwairi, I. Almalkawi, (2021) “Machine Learning-Driven Optimization for Intrusion Detection in Smart Vehicular Networks,” Wireless Personal Communications. https://doi.org/10.1007/s11277-020-07797-y.
[9] A. Joseph, R. Asaletha, V. Manoj, (2026) “Machine Learning‐Based Intrusion Detection and Quantum Cryptography in Vehicular Networks,” International Journal of Robust and Nonlinear Control. https://doi.org/10.1002/rnc.70114.
[10] S. Frimpong, M. Han, W. Zheng(2025) “An adaptive collaborative intrusion detection system for vehicular fog computing networks,” Engineering Applications of Artificial Intelligence. https://doi.org/10.1016/j.engappai.2025.111563.
[11] S. Mehedi, A. Anwar, Z. Rahman, (2021) “Deep Transfer Learning Based Intrusion Detection System for Electric Vehicular Networks,” Sensors. https://doi.org/10.3390/s21144736.
[12] M. Smolin, (2025) “GenCoder++: A Protocol-Aware and Adversarially Robust Adaptive Intrusion Detection Framework for Hybrid CAN-Ethernet Vehicular Networks,” IEEE Access. https://doi.org/10.1109/access.2025.3595879.
[13] G. Visuvanathan, M. Sayeed, S. Yogarayan(2025) “BHFVAL: Block Chain-Enabled Hierarchical Federated Variational Auto Encoder Framework for Secure Intrusion Detection in Vehicular Networks,” Scientific Reports. https://doi.org/10.1038/s41598-025-28560-y.
[14] T. Nandy, R. Md Noor, R. Kolandaisamy, (2024) “A review of security attacks and intrusion detection in the vehicular networks,” Journal of King Saud University – Computer and Information Sciences. https://doi.org/10.1016/j.jksuci.2024.101945.
[15] T. Ragunthar, S. Christila, B. Jyoshna, (2026) “Machine Learning‐Driven Intrusion Detection Systems for Anomaly Detection in Vehicular Ad‐Hoc Networks,” Transactions on Emerging Telecommunications Technologies. https://doi.org/10.1002/ett.70363.
[16] C. Ananth, N. Raj, (2021) “Intrusion Detection System for Energy Efficient Cluster based Vehicular Adhoc Networks,” International Journal of Advanced Computer Science and Applications. https://doi.org/10.14569/ijacsa.2021.0121025.
[17] “Retraction: Intrusion Detection System for Energy Efficient Cluster based Vehicular Adhoc Networks,” International Journal of Advanced Computer Science and Applications, (2025). https://doi.org/10.14569/ijacsa.2021.0121025.retraction.
[18] E. Rodríguez, P. Valls, B. Otero, (2022) “Transfer-Learning-Based Intrusion Detection Framework in IoT Networks,” Sensors. https://doi.org/10.3390/s22155621.
[19] U. Ahmed, J. Lin, G. Srivastava, (2023) “Deep Active Learning Intrusion Detection and Load Balancing in Software-Defined Vehicular Networks,” IEEE Transactions on Intelligent Transportation Systems. https://doi.org/10.1109/tits.2022.3166864.
[20] M. Zhou, L. Han, H. Lu, (2020) “Distributed collaborative intrusion detection system for vehicular Ad Hoc networks based on invariant,” Computer Networks. https://doi.org/10.1016/j.comnet.2020.107174
[21] A. Khalil, H. Farman, M. Nasralla, (2024) “Artificial Intelligence-based intrusion detection system for V2V communication in vehicular ad hoc networks,” Ain Shams Engineering Journal. https://doi.org/10.1016/j.asej.2023.102616.
[22] R. Kim, Y. Kim, (2025) “Trade-Off Model-Based Traffic Sampling for Intrusion Detection in Hybrid Vehicular Networks,” IEEE Transactions on Vehicular Technology. https://doi.org/10.1109/tvt.2025.3567056. [23] M. Khan, V. Ta, H. Rafiq, (2025) “Context-Aware Intrusion Detection in Vehicular Communication Networks: Enhanced Attack Modeling and Dataset,” Applied Artificial Intelligence. https://doi.org/10.1080/08839514.2025.2538453.
[24] R. Swami, M. Dave, V. Ranga, (2020) “Voting‐based intrusion detection framework for securing software‐defined networks,” Concurrency and Computation: Practice and Experience. https://doi.org/10.1002/cpe.5927.
[25] D. Basavaraj, S. Tayeb, (2022) “Towards a Lightweight Intrusion Detection Framework for inVehicle Networks,” Journal of Sensor and Actuator Networks. https://doi.org/10.3390/jsan11010006.
[26] S. Singh, S. Sharma, S. Sharma, (2022) “Intrusion Detection System-Based Security Mechanism for Vehicular Ad-Hoc Networks for Industrial IoT,” IEEE Consumer Electronics Magazine. https://doi.org/10.1109/mce.2021.3138703.
[27] M. Driss, I. Almomani, Z. e Huma, (2022) “A federated learning framework for cyberattack detection in vehicular sensor networks,” Complex & Intelligent Systems. https://doi.org/10.1007/s40747- 022-00705-w.
[28] A. Mabrouk, A. Naja, (2023) “Intrusion detection game for ubiquitous security in vehicular networks: A signaling game based approach,” Computer Networks. https://doi.org/10.1016/j.comnet.2023.109649.
[29] T. Alladi, A. Agrawal, B. Gera, (2023) “Ambient Intelligence for Securing Intelligent Vehicular Networks: Edge-Enabled Intrusion and Anomaly Detection Strategies,” IEEE Internet of Things Magazine. https://doi.org/10.1109/iotm.001.2200197.
[30] S. Wang, B. Zheng, Z. Liu, (2024) “A Lightweight Intrusion Detection System for Vehicular Networks Based on an Improved ViT Model,” IEEE Access. https://doi.org/10.1109/access.2024.3445498.
[31] Harjasdeep Singh, Dr. Durgesh Srivastava, (2023) “Sentiment Analysis: Quantitative Evaluation of Machine Learning Algorithms,” Proceedings of the 5th International Conference on Smart Systems and Inventive Technology (ICSSIT). DVD Part Number: CFP23P17-DVD; ISBN: 978-1-6654-7466- 5.
[32] B.D. Darshan, C.R. Prashanth, (2023) “Dual-discriminator Conditional Generative Adversarial Network Optimized with Hybrid Momentum Search Algorithm and Giza Pyramids Construction Algorithm for Cluster-based Routing in WSN Assisted IoT”, I. J. Computer Network and Information Security,pp. 96- 112.
[33] B.D. Darshan C.R. Prashanth. (May – June (2023)) “Performance Analysis of Cluster-Based Dynamic Multipath Trust Secure Routing (DMTSR)-Protocol in Wireless Sensor Networks (WSNs)”, International Journal of Computer Networks and Applications (IJCNA), Vol. 10, No. 3. DOI:10.22247/ijcna/2023/221891.
[34] JaggannagariKavitha, Komati Thirupathi Rao, (2022) “Dynamic resource allocation in cloud infrastructure using ant lion-based auto-regression model”, Int J CommunSyst, e5071.
[35] Naga SimhadriApparaoPolireddi, J. Kavitha, (May 2023) “Effectiveness of automated chatbots for operational support and self-service based on fuzzy classifier for ASD”, Soft Computing, 13. https://doi.org/10.1007/s00500-023-08541-x.
[36] A. M. Kumar, J. E. Raja, and C. Senthilpari, (Nov. 2025) “Advanced intrusion detection and classification using transfer learning with squeeze-and-excitation network and adaptive optimization in big data,” International Journal of Computer Networks & Communications, Vol. 17, No. 6, pp. 93– 113. doi:10.5121/ijcnc.2025.17606.
[37] S. Vijayalakshmi and V. PrasannaVenkatesan, (Sept. 2025) “Synergy analysis of ensemble feature selection on performance amelioration of intrusion detection system,” International Journal of Computer Networks & Communications, Vol. 17, No. 5, pp. 1–19. doi: 10.5121/ijcnc.2025.17501.


